Granting access early enables us to provide targeted guidance, streamline your preparation, and accelerate your audit readiness.
Create your Audit Package
1. Navigate to the Audit Hub tab and select Create Audit
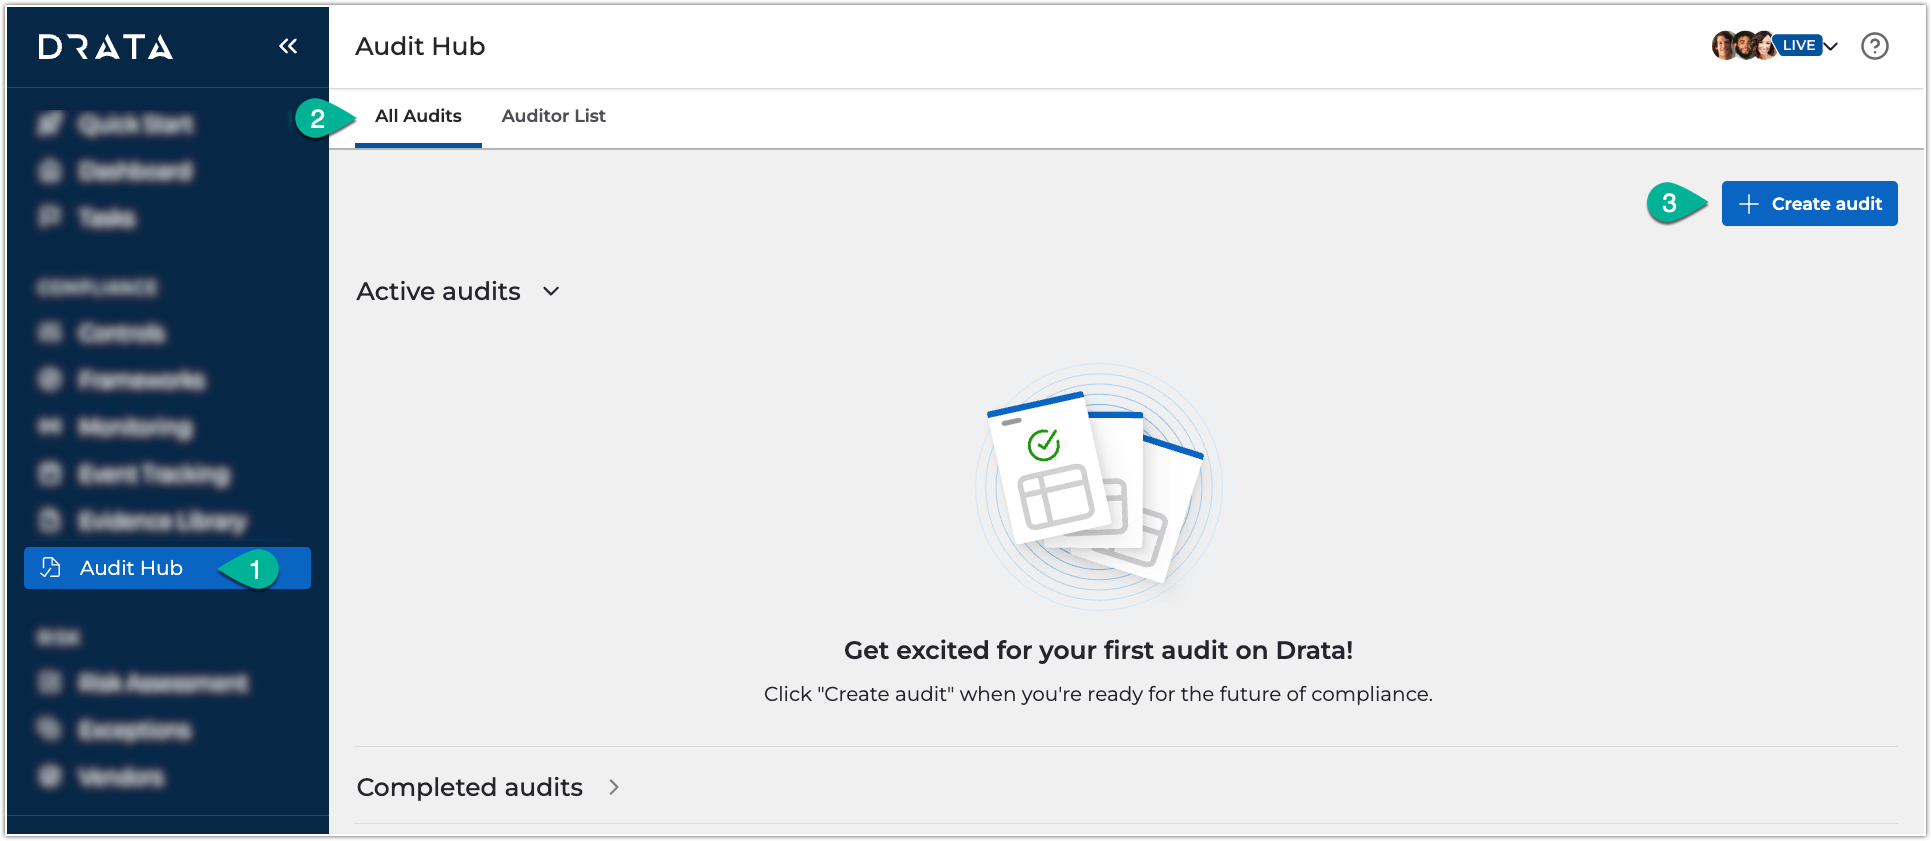
2. Configure your audit parameters:
- Framework: SOC 2 Type 1 or Type 2 (depending on which audit you are doing first)
- Audit firm: Sensiba
- Audit period date:
- For SOC 2 Type 1: select today's date (this can be updated later if needed)
- For SOC 2 Type 2: select a 3 month observation window that you would like to work towards (this can be updated later if needed).
- Additional Frameworks:
-
- If you have engaged Sensiba to perform any other standards alongside your SOC 2 audit, such as GDPR or HIPAA, please follow the above steps selecting the applicable framework (this will be in addition to the SOC 2 audit you create).
-
Grant Sensiba Auditor Access
Once your audit is created, provide access to enable immediate support:
- Navigate to Audit Hub → Open Audit
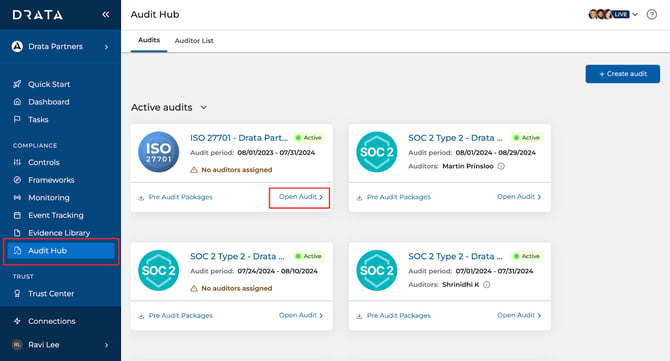
2. Select the edit icon under Assigned Auditors.
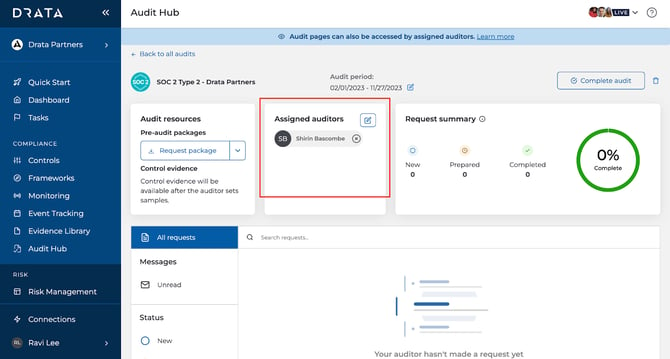
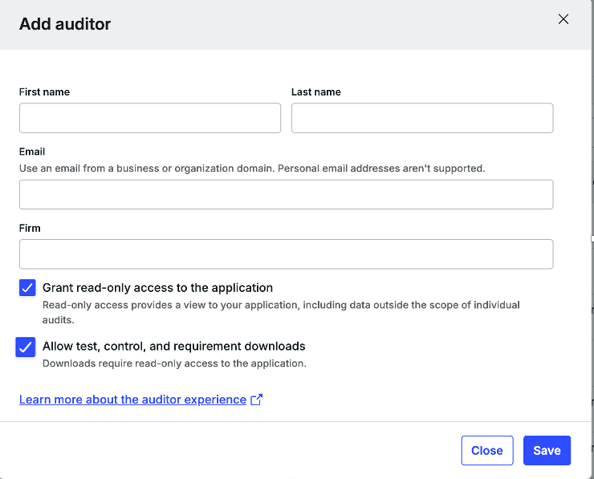
3. Add your auditors:
- GRC Operations - grc@drata.sensiba.com - our AI audit assistant
- Your assigned Lead Auditor (your CSM will share this information with you on your kick off call).
4. Enable the following permissions for all auditors:
- Read-only access
- Download permission for Controls, Tests and Requirements
Once completed the above steps, please notify your Customer Success Manager.
 Need a step-by-step? Watch the Drata Audit Hub Overview for a walkthrough of the setup process.